
HOW TO
Decode and inspect a SAML Response when investigating SAML single sign-on failure
Summary
A SAML assertion, which may be referred to as a SAML response, is an XML document that contains information such as
- User identity (e.g., email, username)
- Authentication status
- Attributes (properties, roles, etc.)
An identity provider (for example, Microsoft Entra) or a service provider (for example, ArcGIS Enterprise) may use the term “claim” when referring to user attributes/properties/roles/etc.
Attempts to automatically create ArcGIS SAML members, or to sign in to ArcGIS using a SAML login, may fail if the attributes included in a SAML response by an identity provider are incorrect.
Details of any error messages generated by the identity provider may be included in the SAML response.
A useful workflow for investigating a SAML authentication failure is therefore to inspect the SAML response.
Note:
This workflow will not work if SAML assertions are encrypted.
Refer to the following help topic: Configure a SAML-compliant identity provider: Advanced settings
Procedure
- Open Developer Tools in a web browser and navigate to the Network page.
- Attempt to sign in to ArcGIS using a SAML login.
- Pause the network log recording.
- Find the signin item.
- The SAML Response is contained within its Payload.
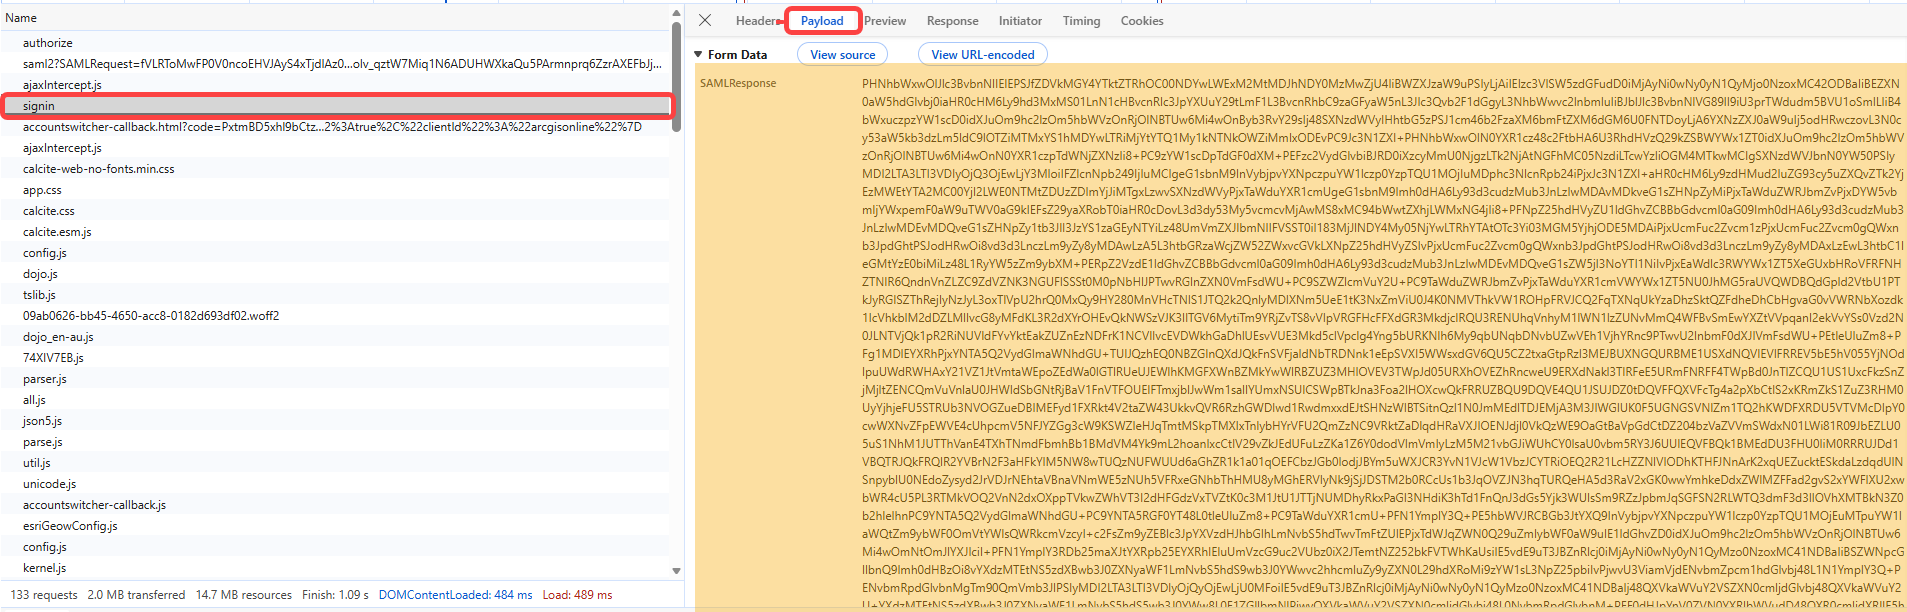
- Paste the SAML Response into a BASE64 Decoder such as: https://www.base64decode.org/
- The XML that is produced by the BASE64 Decoder may be formatted. An example is included below.
- Check the SAML Response for error messages.
- Review the details in the <AttributeStatement> for correctness.
- An incorrect value for the name attribute (http://schemas.xmlsoap.org/ws/2005/05/identity/claims/name) will result in a failed login.
- Check the values for the group attribute (http://schemas.microsoft.com/ws/2008/06/identity/claims/groups); this attribute contains a list of the ObjectIDs of the groups that the user is a member of.
<samlp:Response ID="_d5d0f8a9-e4a8-4460-a13c-02a464330f58" Version="2.0" IssueInstant="2026-07-27T22:47:10.680Z" Destination="https://aws11-5.supportesriau.com.au/portal/sharing/rest/oauth2/saml/signin" InResponseTo="_bSzkMgnvnAUMhJiK"
    xmlns:samlp="urn:oasis:names:tc:SAML:2.0:protocol">
    <Issuer
        xmlns="urn:oasis:names:tc:SAML:2.0:assertion">https://sts.windows.net/e96b131a-a060-4b26-a453-d53d9fb2b181/
    </Issuer>
    <samlp:Status>
        <samlp:StatusCode Value="urn:oasis:names:tc:SAML:2.0:status:Success"/>
    </samlp:Status>
    <Assertion ID="_722e4683-9660-4aa0-977b-70c9b8c81900" IssueInstant="2026-07-27T22:47:10.672Z" Version="2.0"
        xmlns="urn:oasis:names:tc:SAML:2.0:assertion">
        <Issuer>https://sts.windows.net/e96b131a-a060-4b26-a453-d53d9fb2b181/</Issuer>
        <Signature
            xmlns="http://www.w3.org/2000/09/xmldsig#">
            <SignedInfo>
                <CanonicalizationMethod Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
                <SignatureMethod Algorithm="http://www.w3.org/2001/04/xmldsig-more#rsa-sha256"/>
                <Reference URI="#_722e4683-9660-4aa0-977b-70c9b8c81900">
                    <Transforms>
                        <Transform Algorithm="http://www.w3.org/2000/09/xmldsig#enveloped-signature"/>
                        <Transform Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
                    </Transforms>
                    <DigestMethod Algorithm="http://www.w3.org/2001/04/xmlenc#sha256"/>
                    <DigestValue>Wxe1lthTTE4vS6TzBwgVvKd/YuVM+sFPYRI+t3JMlyI=</DigestValue>
                </Reference>
            </SignedInfo>
 <SignatureValue>MSBa0nkiEPX0PtjewemmMONBrDiRe8Qz2272r/z1NUiShkCC1C/Gco42uGq3eKRSCi6Byr09W6nTxMm+sqfebSBx+CLU8dUmQ8zEERBCajMsjRF3h8sJKPdDaGpQWtdw2GcrTPStD5HjVxr3YV7YseCo2d8XPoJa0avmUZjjr6zEoa+4W7v7BK55cBMiGdb5EetV/bKDjFTfq341k+SBVR/pECZHFh8ePK/UA72GyrUirX8bx9mDJ6Xz3/jmCjl3omFpTHuV8XFw==</SignatureValue>
            <KeyInfo>
                <X509Data>
<X509Certificate>MIIC8DCCAdigAwIBAgIQcjWMm4C6y5xJRUr9Yk1tezANBgkqhkiG9w0BAQsFADA0MTIwMAYDVQQDEylNaWNyb3NvZnQhdx7qeiLdQZwh/KlXXYWSlpmdxqNO/tS2ENCeg7gq9ziMY0ehUOr6tqFw5qMVm+G73RmSRSN3T08rFLOhiw4wb+xSwQgBrwtk9b97YIlJoQg2inbjHaR7dKY47vawwyH9XW10d7vtohezXg</X509Certificate>
                </X509Data>
            </KeyInfo>
        </Signature>
        <Subject>
            <NameID Format="urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress">johndoe@mycompany.com </NameID>
            <SubjectConfirmation Method="urn:oasis:names:tc:SAML:2.0:cm:bearer">
                <SubjectConfirmationData InResponseTo="_bSzkMgnvnAUMhJiK" NotOnOrAfter="2026-07-27T23:47:10.540Z" Recipient="https://aws11-5.supportesriau.com.au/portal/sharing/rest/oauth2/saml/signin"/>
            </SubjectConfirmation>
        </Subject>
        <Conditions NotBefore="2026-07-27T22:42:10.540Z" NotOnOrAfter="2026-07-27T23:47:10.540Z">
            <AudienceRestriction>
                <Audience>aws11-5.supportesriau.com.au.portal</Audience>
            </AudienceRestriction>
        </Conditions>
        <AttributeStatement>
            <Attribute Name="http://schemas.microsoft.com/identity/claims/tenantid">
                <AttributeValue>redeacted</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.microsoft.com/identity/claims/objectidentifier">
                <AttributeValue>redeacted</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.microsoft.com/identity/claims/displayname">
                <AttributeValue>John Doe</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.microsoft.com/ws/2008/06/identity/claims/groups">
                <AttributeValue>99999999-9999-9999-9999-999999999999</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.microsoft.com/identity/claims/identityprovider">
                <AttributeValue>https://sts.windows.net/792fc9a4-3964-41a1-8ec8-a09fef7088dd/</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.microsoft.com/claims/authnmethodsreferences">
                <AttributeValue>http://schemas.microsoft.com/ws/2008/06/identity/authenticationmethod/password</AttributeValue>
                <AttributeValue>http://schemas.microsoft.com/ws/2008/06/identity/authenticationmethod/x509</AttributeValue>
                <AttributeValue>http://schemas.microsoft.com/claims/multipleauthn</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname">
                <AttributeValue>John</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname">
                <AttributeValue>Doe</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress">
                <AttributeValue>johndoe@mycompany.com</AttributeValue>
            </Attribute>
            <Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/name">
                <AttributeValue>johndoe@mycompany.com</AttributeValue>
            </Attribute>
        </AttributeStatement>
        <AuthnStatement AuthnInstant="2026-07-27T21:28:24.571Z" SessionIndex="_722e4683-9660-4aa0-977b-70c9b8c81900">
            <AuthnContext>
                <AuthnContextClassRef>urn:oasis:names:tc:SAML:2.0:ac:classes:Password</AuthnContextClassRef>
            </AuthnContext>
        </AuthnStatement>
    </Assertion>
</samlp:Response>
The following links to a document that contains a table listing SAML assertion values and the corresponding Portal for ArcGIS user properties.
Article ID: 000042900
- ArcGIS Enterprise
Get support with AI
Resolve your issue quickly with the Esri Support AI Chatbot.
Related Information
Discover more on this topic

Search for related information

Find training related to this topic

Explore ideas and give feedback
Get help from ArcGIS experts
Start chatting now